SettingsConfiguration
SSO Configuration
OpenID Connect, OAuth 2.0, or SAML sign-in.
SSO Configuration adds an identity provider.
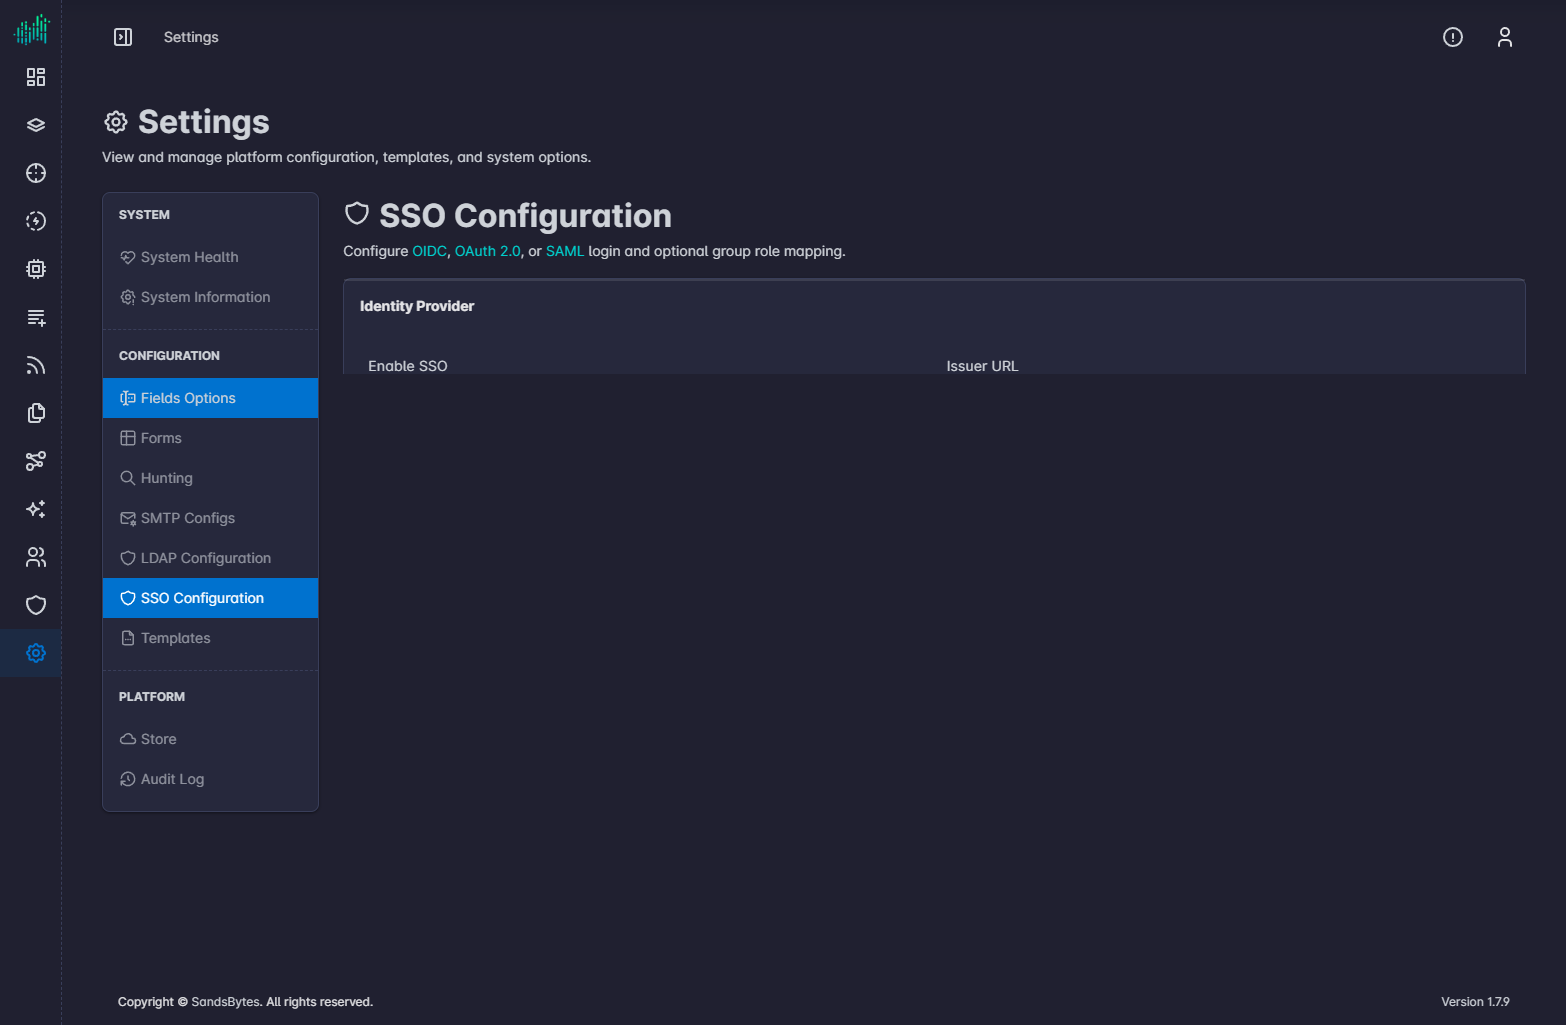
| Control | Purpose |
|---|---|
| Enable SSO | Turns SSO on for this platform. |
| Show Login with SSO | Shows Login with SSO on the login page. |
| Allow SSO Only | Hides username/password and LDAP password login. Keep a break-glass admin session before enabling this. |
| Protocol | OpenID Connect, OAuth 2.0, or SAML. |
| Public base URL | External origin of the API. SandsBytes builds the OAuth redirect URI and the SAML ACS and entity ID from this value. |
| UI base URL | UI origin after the identity-provider callback. Leave blank to use the public base URL. |
| Username claim | Claim or SAML attribute that becomes the username. Default preferred_username. Must be unique. |
| Email claim | Claim that supplies email. Default email. Required the first time an SSO user is created. |
| Groups claim | Claim that lists groups. Default groups. |
| Issuer URL | OIDC issuer base URL. |
| Group role map | Maps an identity-provider group to a local role. |
Save, then use Test Configuration and Open Test Login before you require SSO for everyone.